A manager should be able to approve a holiday request without seeing an employee’s salary history. A finance colleague may need expense data but not performance notes. That is the practical reason to configure role based HR access properly: people get the information and actions required for their job, while sensitive data stays restricted.
For growing businesses, access control often begins informally. A spreadsheet is shared with HR, payroll and line managers because everyone needs “just one thing”. Over time, that creates too many copies of employee data, unclear ownership and a difficult question when someone leaves or changes role: who can still see what?
Role-based access gives HR teams a cleaner way to manage this. Rather than setting permissions person by person, you define roles, assign the right access to each role and review those rules as the organisation changes. The principle is simple. Applying it well takes a little planning.
Start with decisions, not system settings
Before opening your HRIS permission settings, map the decisions each group needs to make. Access should support a responsibility, not simply satisfy curiosity or save someone asking HR for information.
For example, a line manager may need to view their direct reports’ leave balances, approve timesheets and record probation feedback. They do not necessarily need visibility of home addresses, bank details, disciplinary cases or compensation information. A recruiter may need candidate records and interview feedback but not the personnel files of existing employees.
This exercise helps separate data into three useful categories: information employees can manage themselves, information managers need for their teams and information that should remain with HR, payroll, finance or senior leadership. It also exposes exceptions early, such as a country manager who needs reporting across one legal entity but no access to another.
The aim is not to make every process restrictive. It is to make access intentional. When employees and managers can complete routine tasks themselves, HR receives fewer avoidable requests. When confidential information is limited to the right people, privacy risk is lower too.
Define a small set of roles first
Most SMEs do not need dozens of access profiles. Start with a manageable set that reflects how work is actually organised. In many organisations, the first version includes employee, line manager, HR administrator, payroll or finance user, recruiter and senior leader.
An employee role typically allows people to update approved personal details, submit leave and expenses, complete assigned learning and view their own documents. A line manager role adds access to direct reports and actions such as approvals, absence oversight and review inputs.
HR administrators usually need broader access, but even this role may need limits. Someone managing onboarding and employee records may not be the person who should approve salary changes or export payroll data. Separating these duties creates a useful check, particularly as headcount and transaction volume grow.
Avoid creating a new role for every individual preference. That makes administration harder and weakens the consistency role-based access is meant to provide. If one person needs a genuine exception, document why, decide who owns it and set a date to review it.
Use job scope and reporting lines together
A job title alone rarely determines access. Two people called “manager” can have very different responsibilities. Reporting relationships are often equally important because they establish whose data a manager can view or approve.
Your HRIS should therefore reflect accurate organisational structures: managers, departments, locations and where relevant legal entities. If these foundations are unreliable, access rules will be unreliable too. A manager who is incorrectly assigned to a team could see data they should not see, or be unable to approve a time-sensitive request.
Treat organisational data as a controlled process. Define who updates reporting lines, when changes take effect and how temporary arrangements such as acting managers are handled. This is less glamorous than configuring permissions, but it is what makes the permissions dependable.
Configure role based HR access by data sensitivity
Not every field in an employee record carries the same risk. A work phone number and an emergency contact should not automatically be treated alike. When you configure role based HR access, consider both the action someone can take and the sensitivity of the data involved.
A useful approach is to group access around common HR processes:
- Employee profile data: personal contact details, job details, documents and emergency contacts
- Pay and finance data: salary, bank details, expenses, payroll exports and compensation changes
- People management data: leave, time and attendance, objectives, review notes and learning records
- Restricted case data: medical information, grievances, disciplinary matters, right-to-work evidence and investigation notes
The most sensitive category should have the narrowest audience. In many cases, access should be restricted to named HR specialists or authorised leaders rather than a broad HR role. This is especially relevant for special category data under UK GDPR and EU GDPR. Your legal basis, retention rules and access settings need to work together.
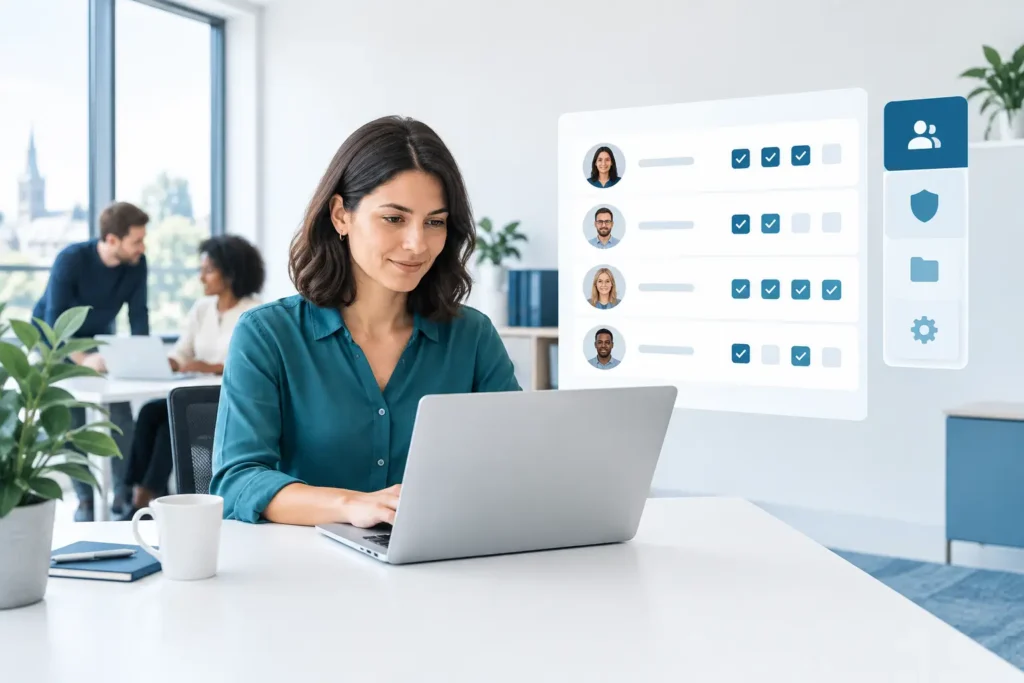
It also helps to distinguish viewing, editing, approving and exporting. Someone may reasonably view a team leave calendar but should not be able to edit another employee’s balance. A finance user may approve an expense but not download an unrestricted employee data export. Export rights deserve particular care because a single file can contain far more data than a single screen.
Build approvals around accountability
Permissions and workflows are closely connected. If access grants a manager the ability to approve a request, the workflow needs to ensure it reaches the correct manager at the correct point in time.
Set clear approval paths for leave, expenses, timesheets, salary changes and sensitive employee changes. Where a request affects more than one function, use staged approvals. For example, a manager can confirm the business need for a salary adjustment, while HR validates policy and finance confirms budget or payroll readiness.
There is a trade-off. Too many approval steps slow people down and encourage workarounds. Too few can leave no meaningful control over spending, pay or personal data. Match the process to the consequence of the decision. A routine holiday request may need one manager approval. A bank-detail amendment may require stronger verification and an audit trail.
Make sure absence cover is configured as well. Managers take leave, move teams and occasionally leave at short notice. A workflow that depends on one unavailable person creates delays for employees and more manual chasing for HR.
Test real scenarios before going live
Permission settings can look sensible on paper while failing in daily use. Test them using realistic scenarios and accounts that represent each role. Do not test only whether a user can access something. Test whether they can complete the entire task without seeing unnecessary information.
Ask practical questions. Can a manager approve a direct report’s leave but not view a colleague’s performance review? Can an employee update their address without changing bank details? Can payroll access required information without being able to edit core employment terms? Can a recruiter move a candidate through the hiring process without opening confidential employee records?
Include edge cases: matrix reporting, employees moving departments, temporary managers, cross-border teams and employees on long-term leave. These are the situations where poorly designed permissions become visible.
Keep a short record of each role, the data it can access, the actions it can take and the person responsible for approving changes. This supports internal governance and makes audits, manager handovers and platform configuration changes far less dependent on one person’s memory.
Review access when people and structures change
Access control is not a one-off implementation task. Joiners, movers and leavers are the moments that matter most. New starters need the right access promptly, employees changing role may need access removed as well as added and leavers should lose access according to a defined timetable.
A quarterly review is a sensible starting point for many growing organisations, with more frequent checks for privileged roles such as HR administration, payroll and finance. Review whether each role still reflects real responsibilities, whether inactive accounts remain and whether any temporary exceptions can now be removed.
This is where a single HR platform has a clear operational advantage. When employee records, organisational structure, leave, performance and expenses sit in separate tools, access changes must be repeated and reconciled. With one source of truth, role changes can feed the processes around them more reliably. Cognitis.cloud is designed around that practical need: one platform, one login and clear control over who sees which HR information.
Good access design should not make work feel harder. It should make the right action easy for employees and managers, while giving HR confidence that private information remains private. Start with the roles you have today, test them against real work and refine them as your organisation grows.